Multi-stage Active Directory reconnaissance and detection
A full red team chain against an AD domain controller (Nmap, password spraying, LDAP and post-compromise enumeration), each step detected in Splunk and mapped to MITRE ATT&CK.
Attack chain
- Username acquisition through social engineering (T1566)
- Network and host discovery with Nmap (T1046, T1018)
- Password spraying over SMB with Hydra (T1110), then a valid login (T1078)
- LDAP enumeration of domain users (T1087)
- Post-compromise enumeration with NetExec
Detection
- The domain controller sends events over TCP 9997, and OPNsense sends syslog over UDP 514.
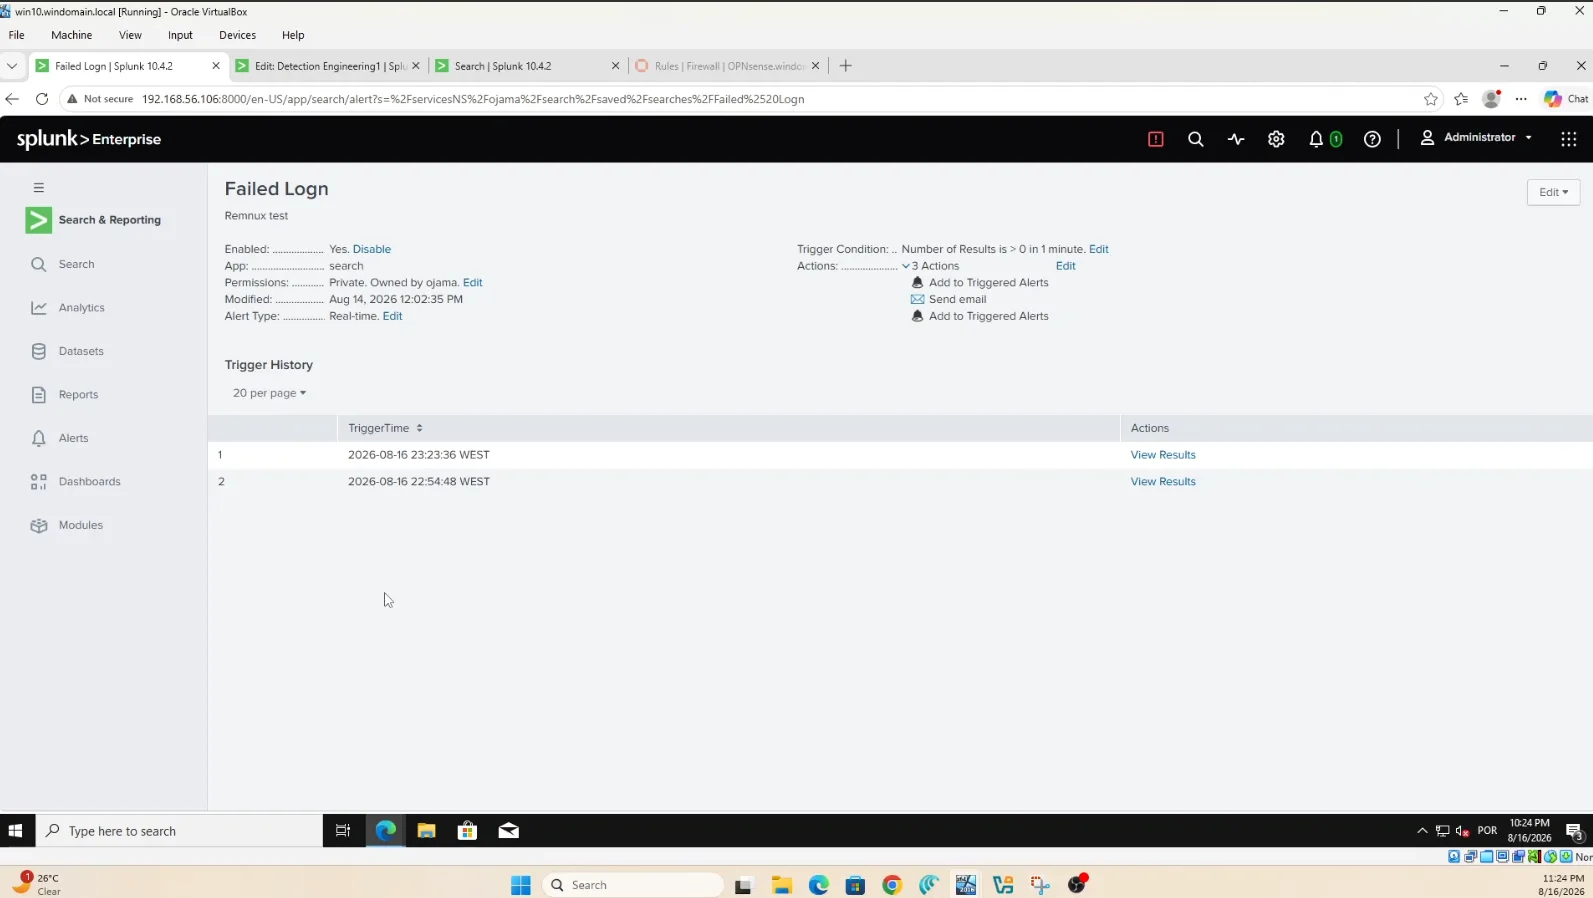
- SPL detections cover failed logons (4625), successful logons (4624) and the spike pattern.
- Correlation searches link the stages together, and dashboards and alerts are tuned to reduce noise.