STRRAT malware PCAP forensics
Network forensic investigation of a STRRAT infection across 11,562 packets, using NetworkMiner triage, a Wireshark decode of the C2 traffic, IOC extraction, OSINT checks and MITRE ATT&CK mapping.
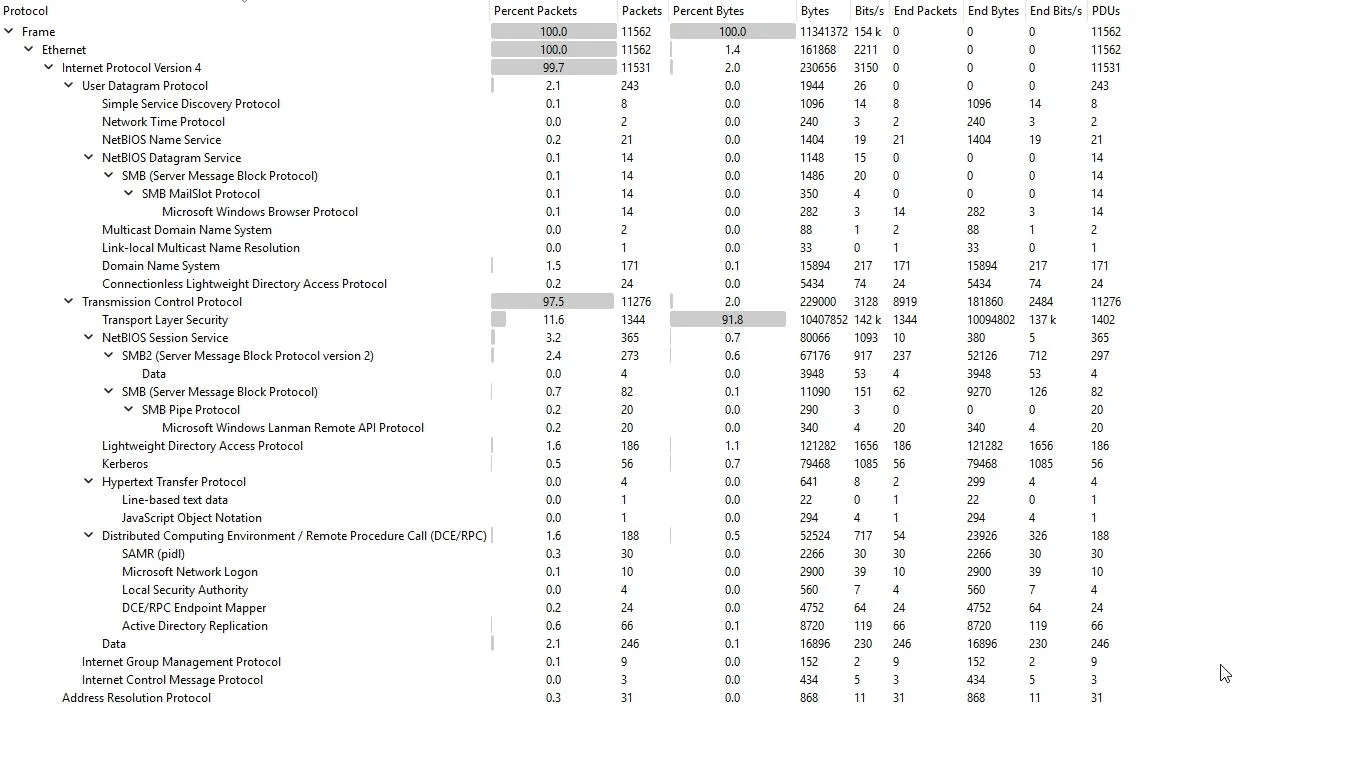
Investigation
- Triage with NetworkMiner to identify hosts, the victim (
DESKTOP-SKBR25F,172.16.1.66) and external contacts, before opening Wireshark. - C2 decode in Wireshark. STRRAT’s custom protocol on high-port TCP to
141.98.10.79:12132, with the bidirectional sessions reconstructed. - Payload decoding with CyberChef, which recovered the system fingerprinting strings the malware sent out.
- OSINT checks with AbuseIPDB and VirusTotal confirmed the C2 infrastructure.
- Detection content. Wireshark filters, Splunk hunting queries and YARA signatures for STRRAT components, all mapped to MITRE ATT&CK.